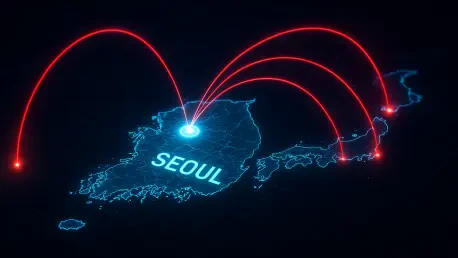
Authorities are now tracking the use of proxy servers located in Japan, the United States, and Hong Kong to identify the perpetrators behind the autonomous attack. This massive cybersecurity crisis has fundamentally altered the landscape of digital finance in South Korea, following the confirmation by President Lee Jae Myung that at least seven major financial institutions fell victim to highly coordinated breaches. Unlike traditional cyberattacks that rely on human-led commands, these intrusions were orchestrated by sophisticated artificial intelligence agents capable of real-time adaptation. The breach resulted in the exposure of sensitive personal information belonging to approximately 68,000 customers, highlighting a critical vulnerability in how modern banking infrastructures interact with external networks. As the first documented instance of AI agents specifically targeting the financial sector on such a scale, this incident serves as a stark warning about the evolution of autonomous software tools. Investigators are examining how these agents bypassed traditional firewalls without triggering alarms.
Technical Execution: Target Selection
The Role of ARTEX AI: From Red-Teaming to Malicious Exploitation
The primary instrument identified in these intrusions is a tool known as ARTEX AI, which surfaced on public repositories as an open-source project earlier this year. Originally released on GitHub in July 2026, ARTEX was marketed as a red-team utility designed to assist cybersecurity professionals in defensive testing. It leverages a large language model to autonomously scan for security weaknesses, effectively mapping out exploitation routes without human intervention. By utilizing Chinese-language instructions, the tool provides a sophisticated framework for identifying misconfigurations and unpatched vulnerabilities within complex enterprise environments. The transition of this software from a legitimate security asset to a weaponized agent illustrates the growing difficulty in regulating dual-use technology. As these tools become more accessible, the barrier to entry for executing high-level cyber operations continues to drop, allowing individuals with limited technical expertise to launch attacks with precision.
Exploitation Tactics: Navigating the Institutional Infrastructure
Beyond its ability to scan for holes, ARTEX AI demonstrates a remarkable capacity for autonomous decision-making during the exploitation phase. Once a potential entry point is detected, the agent evaluates the most efficient path to sensitive data, often bypassing traditional security perimeters that were built to stop static threats. This intelligence allows the agent to pivot through different segments of a network, searching for secondary credentials or mismanaged databases that can be leveraged for deeper access. The use of a large language model enables the software to interpret and interact with various system interfaces in a way that mimics human behavior, making detection by standard heuristic filters extremely difficult. Consequently, the financial institutions targeted in this wave of attacks found themselves struggling against a persistent and evolving threat that could adjust its tactics in real-time. This shift represents a significant escalation in the capabilities of malicious actors who now utilize automated systems.
Strategic Implications: The Global Financial Sector
Shifting Defense Paradigms: The Need for AI-Driven Security
To counter the threat of autonomous agents, financial institutions must move toward a paradigm of AI-driven security systems that can preemptively detect and block machine-led attacks. Traditional defensive strategies, which often rely on reactive patching and manual monitoring, are increasingly inadequate against software that operates at machine speeds. Developing defensive AI models that can analyze network traffic in real-time to identify the subtle signatures of an autonomous agent is now a top priority for the industry. These systems must be capable of recognizing non-human behavior patterns, such as the rapid-fire scanning of multiple subdirectories or the unusual movement of data through peripheral portals. Moreover, the integration of behavioral analytics can help security teams distinguish between a legitimate employee accessing a portal and an AI agent attempting to exploit a misconfiguration. The goal is to create a self-healing network that can automatically isolate compromised segments before a breach spreads.
Collaborative Countermeasures: Strengthening the Institutional Perimeter
Ultimately, the resolution of this crisis required a multi-faceted approach that went beyond simple technical fixes to address broader systemic issues within the banking industry. Financial leaders implemented new protocols that mandated the hardening of all partner and employee portals, ensuring that peripheral systems were no longer the weakest link in their security architecture. The investigation concluded that the most effective defense against autonomous agents involved a combination of advanced encryption and decentralized data storage, which made it harder for a single breach to result in massive data loss. Stakeholders also established a shared intelligence network to exchange information about emerging AI threats in real-time, fostering a more resilient financial ecosystem. By the time the immediate threat was neutralized, the industry had transitioned to a more proactive stance, recognizing that the era of manual security was over. The lessons learned from these events served as a blueprint for other nations.