Traditional security sequences are becoming obsolete as AI agents discover software flaws and initiate exploitation before official patches are even released. This shift has forced the European Central Bank to issue a firm directive to all major financial institutions under its direct supervision. By October 31, 2026, these banks must submit comprehensive action plans detailing their strategies for neutralizing AI-enabled cyberthreats. The urgency stems from the increasing speed at which frontier AI can identify and weaponize vulnerabilities in core banking systems. Since the Digital Operational Resilience Act (DORA) took full effect in January 2025, the pressure to maintain seamless service while defending against machine-speed attacks has intensified. Regulators are no longer satisfied with standard patching cycles; they require proof that banks can survive an environment where the window for defensive response has effectively vanished. Banks must now demonstrate a shift toward active resilience and containment strategies.
1. Document System Connections and Prioritize Critical Digital Assets
Documenting every digital interaction is the foundational requirement for any bank hoping to meet the new regulatory standards. This process involves creating a living inventory of every connection across software applications, server workloads, cloud platforms, and external vendor interfaces. In the current landscape, manual spreadsheets are insufficient for capturing the dynamic nature of hybrid cloud environments. Financial institutions need to utilize automated discovery tools that can visualize real-time data flows and identify hidden dependencies. Understanding the full digital landscape allows security teams to see exactly how data moves through the organization and where potential entry points exist for malicious AI agents. Without this visibility, a bank cannot effectively defend what it does not know exists, making the comprehensive mapping of the network an essential first step. This documentation serves as the blueprint for all subsequent defensive measures and resilience planning efforts.
Once the digital landscape is fully mapped, banks must prioritize their defensive efforts by ranking assets according to their operational importance. It is impossible to protect every system with equal intensity, so focus must be directed toward internet-accessible systems and vital business services that sustain daily operations. Security teams should identify the specific pathways that pose the highest level of risk to the organization, such as those connecting retail banking platforms to legacy back-end databases. By classifying assets based on their criticality and exposure, institutions can allocate their resources more effectively to safeguard the most sensitive data. This hierarchical approach ensures that even during a high-speed AI attack, the most essential functions remain shielded from disruption. Ranking assets also helps in defining the recovery order in the event of a successful breach, allowing the bank to restore customer-facing services with minimal delay while continuing to investigate deeper system compromises.
2. Limit Internal System Movements and Apply Network Segmentation
Restricting lateral traffic is a vital strategy for preventing a localized breach from escalating into a full-scale systemic failure. In many traditional banking architectures, once an intruder gains access to the internal network, they encounter very few obstacles when moving between different systems. To counter this, banks must cut down on unnecessary communication between internal applications, ensuring that if one area is breached, the intruder cannot easily move to surrounding systems. This “least privilege” communication model limits the movement of AI-driven malware, which often seeks to traverse the network to find high-value targets like payment gateways or customer records. By enforcing strict policies on what systems can talk to each other, the bank reduces the overall attack surface and makes the environment significantly more hostile to unauthorized actors. This proactive limitation of east-west traffic is not just a security preference but a core requirement for maintaining operational continuity.
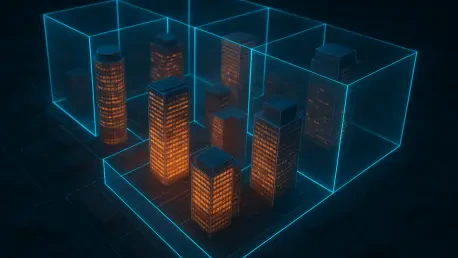
To further bolster these boundaries, banks are expected to apply network segmentation or microsegmentation to wall off their most essential assets. This technique involves creating granular security zones that act as individual compartments, effectively minimizing the potential impact of a security breach. If an attacker manages to compromise a low-priority system, microsegmentation prevents them from jumping to a critical server because the two reside in different, isolated zones. This level of control is particularly effective against frontier AI, which can exploit vulnerabilities faster than human teams can react. By pre-defining these boundaries, the bank builds automated resilience into the very fabric of its infrastructure. The goal is to ensure that a single point of failure does not lead to a catastrophic outage. Implementing these isolation techniques provides a much-needed layer of defense-in-depth, allowing the bank to contain threats at the source and protect the integrity of the broader financial ecosystem.
3. Isolate Suspicious Network Elements and Manage Third-Party Risks
In the event of a confirmed threat, the ability to quarantine compromised or high-risk elements becomes the most critical factor in damage control. Financial institutions must have the technical capability to disconnect or isolate any infected workloads or suspicious third-party links immediately. This prevents a threat from spreading through the network and reaching core processing environments or sensitive customer data repositories. Modern incident response requires more than just manual intervention; it necessitates automated triggers that can sever high-risk connections at machine speed. For instance, if a third-party vendor’s environment is compromised, the bank’s systems should be able to instantly revoke its access without waiting for a manual review. This rapid isolation acts as a “circuit breaker” for the digital infrastructure, preserving the majority of the bank’s operations while the specific threat is analyzed and eradicated. Maintaining this level of agility is essential for surviving the compressed exploitation timelines.
Managing these third-party risks requires a deep understanding of the dependencies that extend beyond the bank’s own data center. A vulnerability in a cloud service provider or a managed software component can create a direct path to a bank’s critical services if not properly contained. To address this, banks must implement controls that assume a vendor’s environment could be compromised at any time. Rather than relying solely on annual audits or security certifications, institutions are moving toward real-time monitoring of external connections. When an anomaly is detected in the traffic coming from a partner, the system should automatically restrict that connection to a minimal set of necessary functions. This approach ensures that the bank remains operational even if its supply chain is under attack. By treating every external link as a potential vector for lateral movement, banks can significantly reduce their “blast radius” and maintain the trust of their customers and regulators alike.
4. Evaluate Emergency Protocols Against Modern AI-Driven Threats
Proving resilience also requires banks to evaluate their emergency protocols against modern, AI-driven threats through rigorous testing. Organizations must run simulations to see how their response plans hold up against rapid exploitation, ransomware, cloud failures, and disruptions in the supply chain. These drills should go beyond basic disaster recovery and instead focus on the specific challenges posed by automated agents that can pivot and adapt faster than traditional scripts. By testing these scenarios, banks can identify gaps in their containment strategies and refine their communication plans for both internal stakeholders and regulators. It is no longer enough to have a plan on paper; it must be proven effective under the pressure of a simulated high-velocity attack. Continuous testing ensures that the bank’s security posture remains aligned with the evolving capabilities of frontier AI, providing the data necessary to update action plans regularly.
Furthermore, these evaluations must include the human element of the response team, ensuring that IT and security staff are trained to work alongside automated containment systems. AI-driven attacks often involve sophisticated social engineering or “vishing” components designed to bypass technical controls. Resilience testing should therefore incorporate multi-vector scenarios that challenge the bank’s ability to identify and neutralize complex, multi-stage intrusions. The insights gained from these simulations allow institutions to fine-tune their detection thresholds and improve the speed of their decision-making processes. A bank that has successfully tested its ability to isolate a compromised cloud environment in minutes is far more likely to survive a real-world incident without a significant service outage. Ultimately, these rigorous evaluations provide the confidence needed to meet the European Central Bank’s stringent requirements and demonstrate a true state of operational readiness.
Operational Resilience as the Final Defensive Standard
The European Central Bank’s mandate established a clear path forward for the industry, emphasizing that passive defense was no longer a viable option. Financial institutions that prioritized these resilience strategies moved beyond the impossible goal of perfect prevention and instead focused on the reality of containment. They discovered that by implementing automated isolation and granular segmentation, they could protect their most vital services even when perimeter defenses were breached. The lessons learned from this transition highlighted the importance of moving toward a zero-trust architecture where every connection is verified and every workload is isolated. Banks that succeeded in meeting the 2026 requirements did so by integrating security directly into their operational workflows, ensuring that resilience was a constant feature rather than a reactive measure. Moving forward, the industry must continue to refine these containment models to keep pace with the increasing sophistication of AI agents. Resilience is now a permanent operational standard.