The exploitation of a backup access page at the South Korean Financial Security Institute allowed hackers to bypass multi-factor authentication protocols. This sophisticated intrusion targeted the very organization tasked with shielding the nation’s financial infrastructure from external threats, creating a paradoxical security failure that reverberates through the regional banking sector. By identifying a specific weakness in the login architecture, the perpetrators demonstrated that even the most robust defenses often possess overlooked secondary entry points designed for convenience or emergency recovery. The incident is particularly concerning because the Financial Security Institute serves as a central hub for threat intelligence, meaning any compromise of its internal systems potentially exposes the defensive strategies used by major banks and cryptocurrency exchanges. This breach highlights a strategic shift among modern cyber adversaries who now focus on high-value gatekeepers rather than individual consumer accounts.
Anatomy of the Backup Page Exploitation
The attackers managed to infiltrate the system by impersonating a high-ranking official from the Financial Supervisory Service, leveraging the perceived authority of the regulatory body to navigate internal permissions. This social engineering component was paired with a technical exploit involving a legacy backup page that was intended to facilitate access when standard text-message authentication failed. By utilizing this secondary pathway, the hackers were able to sidestep the rigorous multi-factor protocols that usually protect the Continuous Evaluation Support System. This specific platform is a critical resource used by approximately 3,000 firms annually to conduct mandatory security reviews and submit compliance documentation. Once inside, the perpetrators did not remain stationary; instead, they rotated through more than 100 distinct IP addresses to mask their movements and blend in with legitimate administrative traffic. This level of operational security allowed the breach to persist until flagged by behavioral analysis.
During the period of unauthorized access, the hackers focused on sensitive administrative documentation rather than direct financial assets or ledger entries. Specifically, the leak involved approximately 200 administrative forms and over 650 records containing the personal information of security employees at roughly 40 different financial firms. These records included full names, dates of birth, and mobile phone numbers, providing the attackers with a treasure trove of data that could be used for future spear-phishing campaigns or credential harvesting. While the Financial Security Institute emphasized that internal network diagrams and sensitive customer transaction logs remained untouched, the theft of employee data creates a secondary layer of risk. By cataloging the individuals responsible for security at South Korea’s largest banks, the attackers effectively created a roadmap for future social engineering attempts. The precision of the data theft suggests a long-term strategic objective rather than a simple opportunistic strike.
Strategic Defensive Upgrades and Industry Resilience
In the immediate aftermath of the discovery, the Financial Security Institute took decisive action by shuttering the vulnerable portal and initiating a comprehensive audit of all secondary access points. Investigators spent several weeks tracing the origin of the 100 IP addresses used in the attack, though the ultimate source remained obscured by sophisticated spoofing techniques frequently associated with state-sponsored actors. The agency acknowledged that the existence of an unmonitored backup access page represented a significant procedural failure that should have been caught during internal reviews. To mitigate the impact on affected personnel, the institute pledged to provide compensation for any secondary harm resulting from the leak of employee information and implemented enhanced monitoring for the compromised identities. Furthermore, regulators recommended that financial firms move their most critical assets into offline cold storage to prevent any possibility of remote theft following the breach.
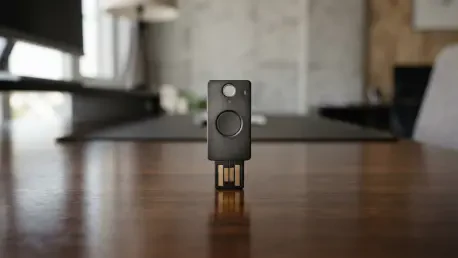
Following the breach, the financial sector recognized the necessity of pivoting toward more resilient and decentralized security models to ensure that a single point of failure no longer compromised the entire ecosystem. One practical solution involved the mandatory transition from text-based multi-factor authentication to hardware-based security keys or decentralized identity solutions that proved less susceptible to bypass exploits. Organizations also prioritized the elimination of all backup access pages in favor of strictly audited, multi-person authorization processes for administrative tasks. Frequent and unannounced red-team exercises were identified as essential tools to help identify hidden architectural vulnerabilities before they were discovered by malicious actors. Additionally, financial institutions enhanced their cross-border threat intelligence sharing to better track the evolving tactics of hostile groups. These proactive strategies ensured that the gatekeepers strengthened their defenses against future aggression.